Friday, June 17, 2011

U.S. Government In Cyber Fight But Can't Keep Up

U.S. Government In Cyber Fight But Can't Keep Up

Us Cybersecurity


By Phil Stewart, Diane Bartz, Jim Wolf and Jeff Mason
WASHINGTON (Reuters) - The Pentagon is about to roll out an expanded effort to safeguard its contractors from hackers and is building a virtual firing range in cyberspace to test new technologies, according to officials familiar with the plans, as a recent wave of cyber attacks boosts concerns about U.S. vulnerability to digital warfare.
The twin efforts show how President Barack Obama's administration is racing on multiple fronts to plug the holes in U.S. cyber defenses.
Notwithstanding the military's efforts, however, the overall gap appears to be widening, as adversaries and criminals move faster than government and corporations, and technologies such as mobile applications for smart phones proliferate more rapidly than policymakers can respond, officials and analysts said.
A Reuters examination of American cyber readiness produced the following findings:
* Spin-offs of the malicious code dubbed "agent.btz" used to attack the military's U.S. Central Command in 2008 are still roiling U.S. networks today. People inside and outside the U.S. government strongly suspect Russia was behind the attack, which was the most significant known breach of military networks.
* There are serious questions about the security of "cloud computing," even as the U.S. government prepares to embrace that technology in a big way for its cost savings.
* The U.S. electrical grid and other critical nodes are still vulnerable to cyber attack, 13 years after then-President Bill Clinton declared that protecting critical infrastructure was a national priority.
* While some progress has been made in coordinating among government agencies with different missions, and across the public-private sector gap, much remains to be done.
* Government officials say one of the things they fear most is a so-called "zero-day attack," exploiting a vulnerability unknown to the software developer until the strike hits.
That's the technique that was used by the Stuxnet worm that snarled Iran's enriched uranium-producing centrifuges last summer, and which many experts say may have been created by the United States or Israel. A mere 12 months later, would-be hackers can readily find digital tool kits for building Stuxnet-like weapons on the Internet, according to a private-sector expert who requested anonymity.
"We're much better off (technologically) than we were a few years ago, but we have not kept pace with opponents," said Jim Lewis, a cyber expert with the Center for Strategic and International Studies think tank. "The network is so deeply flawed that it can't be secured."
"IT'S LIKE AN INSECT INFESTATION"
In recent months hackers have broken into the SecurID tokens used by millions of people, targeting data from defense contractors Lockheed Martin, L3 and almost certainly others; launched a sophisticated strike on the International Monetary Fund; and breached digital barriers to grab account information from Sony, Google, Citigroup and a long list of others.
The latest high-profile victims were the public websites of the CIA and the U.S. Senate - whose committees are drafting legislation to improve coordination of cyber defenses.
Terabytes of data are flying out the door, and billions of dollars are lost in remediation costs and reputational harm, government and private security experts said in interviews. The head of the U.S. military's Cyber Command, General Keith Alexander, has estimated that Pentagon computer systems are probed by would-be assailants 250,000 times each hour.
Cyber intrusions are now a fact of life, and a widely accepted cost of doing business.
"We don't treat it as if it's here today, gone tomorrow," said Jay Opperman, Comcast Corp.'s senior director of security and privacy. "It's like an insect infestation. Once you've got it, you never get rid of it."
The private-sector expert who requested anonymity said a top official at a major Internet service provider told him that he knew his network had been infiltrated by elite hackers. He could digitally kick them out - but that would risk provoking a debilitating counter-attack.
"THE THING ... THAT KEEPS ME UP AT NIGHT"
The idea behind the soon-to-be-announced Pentagon program for defense contractors is to boost information-sharing with the Defense Department on cyber threats. It also aims to speed reporting of attacks on firms that make up what the Pentagon calls the Defense Industrial Base.
The DIB, as it is sometimes known, provides the Defense Department some $400 billion a year in arms, supplies and other services. The new program is voluntary and builds on a smaller pilot, reflecting the persistent challenge of regulating private firms that traditionally shield proprietary data and often downplay cyber setbacks.
Ultimately, the new program may lead to agreement to put at least some Pentagon contractors behind military-grade network perimeter defenses, such as those that protect the Pentagon's own classified networks.
On another front, the Pentagon's far-out research arm, the Defense Advanced Research Projects Agency, is expected to launch by mid-2012 the National Cyber Range, a kind of replica of the Internet costing an estimated $130 million that would be used to test cutting-edge cyber defense technologies and help train cyber warriors.
The Obama administration has made cyber security a national priority, and tried to fashion an "all-government response" that imposes order on the competing domains and priorities of the Pentagon, FBI, Department of Homeland Security, the super-secret National Security Agency and the private sector.
"We're far better prepared than we've ever been before," said White House cybersecurity coordinator Howard Schmidt.
"Notwithstanding all the threats that we see out there, the things that are making news on a regular basis about a company that's been intruded upon ... (look at) how much the system still runs," Schmidt told Reuters in an interview.
The key, Schmidt said, is resiliency, "to make sure that we're better prepared, to make sure that the disruptions when they do occur are minimum - we're able to recover from them."
Still, he said major worries remain. "The thing that I worry about that keeps me up at night is the unknown vulnerability that may exist out there."
Some officials are even less sanguine.
The Pentagon's computer systems are widely considered to be better protected than other U.S. government agencies', and far safer than the private sector's. Still, a U.S. defense official told Reuters he would give the Pentagon just a "C+" grade overall for its cyber defenses. "We're not impervious to attack by any stretch, but nor are we 'open kimono'," the official said. He added: "And we're getting better."
WHAT IS 'CYBER'?
Experts say that one of the toughest challenges of cyber defense is, oddly, definitions. What constitutes "cyber"? Computers and digital networks, certainly. But how about digitized pictures or video streams from a pilotless Predator drone flying over Pakistan?
Who is responsible for protecting what? Where does national security begin and privacy end?
"The other big problem is lack of policy," said one former U.S. official. "(We) lack policy because we lack consensus. We lack consensus because we haven't had an informed debate. We lack an informed debate because we don't have a common pool of data. And we don't have a common pool of data because we don't share it."
Nowhere is the problem more acute than in thinking about cyber warfare. What constitutes an act of war in cyberspace? And how do you determine who it was that fired the shot?
U.S. military officials, eager to talk about how the Pentagon has boosted computer defenses, clam up when the topic turns to offensive capabilities.
The Pentagon has put together a classified list of its cyber capabilities so policymakers know their options - just as it does for more conventional weapons.
Offensive actions against foreign systems would require White House authorization. But the Pentagon does not need special approval to do the kind of cyber surveillance work that can identify vulnerabilities in foreign networks, a U.S. official told Reuters, speaking on condition of anonymity.
That includes leaving hidden digital "beacons" inside adversaries' networks that could be used to pinpoint future targets. The beacons can phone home to tell U.S. military computers that they are still operational, the official said.
While the United States is trying to apply conventional military logic to the cyber realm, there is no global consensus about the rules of cyber war. A Pentagon report due out toward the end of the month is not expected to articulate case-by-case possibilities of when a cyber war could turn into a real one.
INTO THE CLOUD
Even as such policy debates rage, the technological landscape is being remade, seemingly by the month, posing new challenges - and opportunities. Tens of thousands of mobile applications for smartphones and tablet computers represent new vectors for hacks and attacks.
"The quick answer is we haven't been doing enough and we're semi-late to the game" on protecting mobile applications, said Rear Admiral Mike Brown, a senior Department of Homeland Security cyber security official.
U.S. government agencies are working with major commercial vendors "to start looking together at how to address the issues of mobile vulnerabilities," Brown said at a symposium sponsored by Symantec Corp.
Meanwhile, the U.S. federal government is planning to move in a big way into "cloud computing," in which off-site providers offer network and storage resources accessible remotely from a variety of computing platforms.
Potential cost savings are significant. Handled correctly, computing clouds could offer added security, specialists say. But there are also risks.
A study released in April by CA Technologies and the Michigan-based Ponemon Institute contained alarming findings. Based on a survey of 103 U.S. and 24 European cloud computing providers, it found that a majority did not view security of their services as a competitive advantage, and believed that security was their customers' responsibility, not theirs.
Most did not have dedicated security personnel on staff.
Deputy Defense Secretary William Lynn met Google executives in California in mid-February to discuss cloud computing. On May 19, Lynn instructed the Pentagon's Defense Science Board to study the benefits and risks of cloud computing, "paying particular attention to attacks on communications that would destroy or delay delivery of services and information for time-critical uses."
Lynn told Reuters that "cloud computing has the potential to offer greater capability at equal or lesser costs." He added: "I want to make sure we are taking full advantage of these advanced technologies."
The Pentagon is preparing a cloud computing strategy, which it expects to complete by the end of the summer, a U.S. defense official told Reuters.
"We're trying to get to the place where warfighters or any of us can get to our information from anywhere on the planet, with any device," the official said.
Schmidt, the White House coordinator, said as many as 170 security controls are being built into government cloud computing projects from the start. "It's not deploying something and securing it later. We're setting the requirements at the outset."
"I'M NOT CONFIDENT THAT WE WOULD KNOW..."
So how safe are the computer networks of the United States, which perhaps more than any nation relies on them for banking, electric power and other basics of modern civilization?
In May 1998, then-President Clinton signed Presidential Decision Directive 63, calling for a "reliable, interconnected, and secure" network by 2003, and establishing a national coordinator for protecting critical infrastructure.
The Department of Homeland Security now has lead responsibility for protecting the power grid. Yet, as with almost everything involving cyber, it's not quite that simple.
If there were a cyber attack on the power grid today, "I'm not confident that we would know what parts of the government should respond," said one former U.S. official, who asked not to be identified. "Who jumps in there? DHS, DoD, Cyber Command, NSA, the intelligence community?"
"So nothing's really happened." said former Pentagon general counsel Judith Miller, talking about grid vulnerability at a cyber event in Washington this month.
"This is a discussion we had in the 1990s. We're having it right now. Nothing really has changed, although perhaps the ability of attackers, whether they're nation states or just kids, has grown apace," she said.
A central conundrum is that the Pentagon's National Security Agency, which specializes in electronic eavesdropping, has personnel with the best cyber skills, but has been until recently mostly shut out of protecting domestic networks. That's due to the highly classified nature of the NSA's work, and fears that it will stray into domestic spying.
Another complicating factor: the 1878 Posse Comitatus Act, which generally bars federal military personnel from acting in a law-enforcement capacity within the United States, except where expressly authorized by Congress.
"NSA has a long history in cyber security, on both the offensive and the defensive sides. It has great resources and expertise. But it makes privacy advocates nervous," said Stewart Baker, a former DHS official now at the law firm Steptoe and Johnson LLP.
Last October, the Defense Department and Homeland Security - responsible for protecting civilian U.S. government networks - signed a memorandum to cooperate, with the NSA sharing technology and the agencies swapping personnel.
The effort has gotten mixed reviews. Schmidt said that early reports of inter-agency tension have dissipated, and Representative James Langevin, a member of the House intelligence committee, said DHS is improving. "I don't think that they're there yet but we're moving in the right direction," he said.
However other experts, who would not be quoted for the record, said the gap between the two agencies remains wide.
Even if the NSA, DHS and other agencies worked together seamlessly, the problem remains of coaxing industries in critical infrastructure to accept more government regulation.
"There's absolutely no question that the power companies and indeed state regulators have been unenthusiastic about a federal role," Baker said. He added this warning: "The regulation that would pass after a disaster is a lot worse than they would get right now."
And then there's the Stuxnet-like "zero day" attack, exploiting a flaw no one knew existed, perhaps tucked into some off-the-shelf software like that purchased daily by federal agencies.
"Our largest fear ... is the zero day attack," said Sherrill Nicely, the CIA's deputy chief information officer. "It's very, very, very difficult to protect oneself from an attack that you did not know was coming or the vulnerability that you did not know existed."
(Additional reporting by Jeremy Pelofsky and Warren Strobel; Writing by Warren Strobel; Editing by Kristin Roberts and Claudia Parsons)
Copyright 2011 Thomson Reuters. Click for Restrictions

Wednesday, June 15, 2011

"Anonymous": A meeting with A Member


Giving A Face To 'Anonymous': 

A Meeting With A Member Of The Secret Society Of Hackers

Protest
First Posted: 06/15/11 12:22 PM ET Updated: 06/15/11 12:25 PM ET


Here's the thing about the secret international brotherhood of Internet bandits called Anonymous: It's kind of hard to get an interview with them. When you offer revolutionary groups a chance to say their piece to a mass audience, they generally get back to you within two to three hours, but Anonymous isn't a group.
Or that's what they'd say, anyway, if you could get them to talk. Most of the time they don't, except in 1980s robot voices. But more on that later.
There's been a lot of curiosity about Anonymous lately, and fortunately for the inquiring journalist, lots of non-anonymous people have been talking about them. The most recent flurry of chatter began on Friday, when police in Spain said they'd hunted down three members of the group (or the alliance, or whatever you want to call them), which had incurred Spain's wrath back in March by temporarily knocking out the website of the national government.
Then, on Monday, it was announced that the Turkish police had captured 32 additional suspected members. A few days before, Anonymous had taken over the website of the Turkish Telecommunications Authority and shut it down. In other words, if you went to the national telecommunications website that day to find out why your phone wasn’t working, you instead found that the website wasn't working, and you had a tantrum.
And then, on Monday and again Tuesday, came the reports that hit closest to home: Anonymous was going after the Federal Reserve. Even for a group that essentially set off a series of attacks that brought the multinational giant Sony to its knees in April, this seemed like awfully big prey. Yet if you doubt the group's ability to do damage to a powerful adversary, you probably don't realize that it's already landed big blows against some pretty sizable opponents – to begin with, Sony, and MasterCard, and Iran. Or that its members recently broke into the website of HBGary, an internet security firm whose CEO threatened to out Anonymous members, and published 50,000 internal emails and the CEO's social security number, humiliating him into resigning from the company.
As astute observers will point out, the news of Anonymous' declaration of war against the Federal Reserve actually arrived on Saturday, when the group posted a YouTube video that opened with a clip of Fed Chairman Ben Bernanke reassuring a journalist that he had the problem of the growing gap between rich and poor "under control." This clip was followed by a voice-over manifesto against the bank, accompanied by a series of title cards and delivered in the voice of a robot as might be imagined by a director of 1980s B-movies.
But the story didn't really take off until Tuesday, when a series of articles in the tech press noted that the group planned go to battle that day -- both by hacking into the bank's website and by staging a series of old-fashioned protests at different banks around the country. And so, that day, an inquiring journalist set out to track down the shadowy syndicate. Or the secretive fraternity. Or whatever.
Calls were made to security researchers (hackers employed by the "good guys"). Tweets were cast out into the waves of the Internet. And then, at about 9:30 that night, after hours of silence, an answer arrived in the form of an email: Go to the Manhattan Municipal Building. There would be people there. Ask for "Gary in the White Hat."
First, a little history: Anonymous started about eight years ago on the imageboard of 4chan.org, a website where people posted random pictures of things they thought were shocking or worthy of "lulz," a.k.a. laughs. (Often these things were porn.) In 2008, a consort of some of the more devoted pranksters who'd found one another on the site declared war against the Church of Scientology, accusing it of censorship for removing an unflattering video of Tom Cruise from YouTube.
Protests were organized: demonstrators showed up to the Church's headquarters wearing masks portraying the grinning visage of the 17th-century English icon of anarchy Guy Fawkes. But the group's main battlefield was always the Internet. In December, the group attacked the websites of MasterCard and PayPal, whose executives had provoked them by suspending payments to WikiLeaks, which Anonymous members saw as a comrade in the fight against censorship.
And in April, after Sony PlayStation antagonized the group by suing a hacker who'd found a way to run third-party applications on its gaming consoles, Anonymous struck again, essentially commanding an army of Internet drones to bombard the company's website with automated information requests until the site was knocked offline. The group also claimed responsibility for publishing more than 10,000 emails stolen from a website of the Iranian government, and it's been said that they helped the agitators in Tunisia circumvent the online barriers that that the government there had thrown up in the revolution's path.
Traditionally, hackers have divided themselves into two groups: the "black hats," who exploit the vulnerabilities of their marks for profit, and the "white hats," who hire themselves out to protect the vulnerable. Anonymous fits into neither category. Some people call them "gray hats," but that implies an level of cohesion they tend to deny. In their online communications they insist they have no leader, no chain of command. Anyone who claims to be acting under the banner of Anonymous is by virtue of that fact a member of Anonymous.
And yet, the hat work by Gary in the White Hat was indeed white. It had a full brim and a band around it, and that was the extent of any similarities between the wearer and Jack Nicholson's character from "Chinatown." Gary, as he asked to be called, was built like Roman Polanski, with rectangular glasses and a beard that hadn't been trimmed in a month. He was locking up a bike outside the municipal building while a crowd of about 60 people, mostly kids in their teens and twenties, sat on the ground a little ways off, in a sprawl of backpacks and sleeping mats and guys with congas. A teenage girl was overheard inquiring, "Does anyone know the words to 'This Land Is Your Land'?"
Most of these people were not with Anonymous, Gary said. He explained that he had initially intended to hold his protest in a park a few blocks away, closer to the Federal Reserve, but several factors had intervened, including what Gary described as a corporate barbecue. Ultimately, he'd decided to merge his contingent of about twenty Anonymous supporters with a slightly larger mass of protestors who had set up camp under the eaves of the municipal building that night for a "sleep-in" demonstration against the mayor's proposed budget cuts.
"Anonymous is a decentralized group," Gary said, lighting a cigarette. "They have all sorts of different motives. There are those who are hackers, those who are activists, those who are 16-year-old kids wanting to impress their girlfriends." In general, the members rally around the belief that "people who hoard information are the same people who hoard wealth."
You can now forget that earlier claim about Anonymous' reluctance to talk: Gary talked so much that he kept having to dig into his pocket for his matches so he could relight his cigarette. He said that he'd gotten involved with Anonymous a couple of months ago, when he saw something on the Internet about how they were planning a campaign against the country's central banking system and the banking industry in general, and were demanding that Bernanke step down. He wanted to help them "knock the corporations out of the government."
A year before that, Gary was working in real estate. "I made a lot of money and I lost a lot of money," is how he summed it up. His employer, he said, was a company that invested half a billion dollars buying up slum buildings in Upper Manhattan and the Bronx: "A slumlord, basically. They were trying to turn lead into gold."
He came to believe that "the people who rise to the tops of these corporations are basically sociopaths – they have no concept of right or wrong, they just want to make the boss happy."
In any event, the corporation's adventure in alchemy didn't pan out very well, and Gary was laid off last May. After a stint on unemployment, things got to the point where he was facing homelessness, so he set off on a bike ride down to Florida, camping out on private land at the invitation of strangers.
When he learned about Anonymous' battle against the banks he began trying to contact the group over Twitter. Eventually someone sent a reply saying they could use his help answering emails. Gary agreed to pitch in, and suggested to his unknown interlocutor that they supplement their online actions with a public protest near Wall Street.
He started a Twitter account devoted to promoting this idea -- @NYCcamp –- and soon began receiving messages from people around the country who said they wanted to hold protests of their own to coincide with his.
Outside the Manhattan Municipal Building on Tuesday night, Gary said he wasn't sure how those other protests had fared, and he admitted that the turnout at his own rally wasn't quite what he'd hoped for, but he didn't seem too disappointed. It is an article of faith among Anonymous members that, as their motto goes, Anonymous is legion. And besides, Gary had learned on Twitter a little while earlier that at least one additional Anonymous member had joined the gathering. He looked around at the crowd. "I have no idea who she is," he said.


Note: This article is from . The Huffingtonpost

Tuesday, June 14, 2011

Hackers LulzSec Attacks Escapist Magazine, EVE Online & MineCraft

LulzSec attacks Escapist Magazine, EVE Online, and Minecraft


Hacker group LulzSec, the same group that's attacked Sony and Nintendo in the past, has tweeted that it's committed three distributed denial of service attacks against gaming companies today, bringing down EVE Online's Tranquility server, Minecraft's multiplayer services, and the Escapist Magazine's website. EVE Online's CCP has confirmed both the outage and the attack, the Escapist is unreachable at the moment, and Minecraft creator Notch says that things were down, but supposedly service has been restored.

LulzSec hasn't shared a reason for the attacks just yet, but we can only guess it's, as they say, "for teh lulz."

Tetris goes 3D on PSN today, 3DS in October

Tetris goes 3D on PSN today, 3DS in October


If you run to your PS3 now and fire up Tetris, you'll be presented with the option to update. Download that 75MB file and -- just like that! -- you'll be playing in 3D. Oh, also, you have to have a 3D television and be wearing your glasses. We should really have told you about that part first.

In other 3D Tetris news, right before E3 the Tetris Company announced plans to localize Hudson's Tetris Axis for 3DS this October, claiming that it "will allow fans to experience the game like never before – in 3D!" Now, by the time that comes out, fans will already have experienced it through the PS3 version, rendering that hyperbolic press release statement inaccurate.

To be fair, though, it was already inaccurate, because the Virtual Boy's V-Tetris got there first, in1995.

Monday, June 13, 2011

Bethesda Announces... They Were Hacked

What's Going on?! It seems like Gamers' are the "IN" thing for Hacking. PlayStation Network, Nintendo and now online Bethesda. Here is their Blog Post:


Please Read: Hack attempts against our websites and forums

Over the past weekend, a hacker group attempted an unlawful intrusion of our websites to gain access to data. We believe we have taken appropriate action to protect our data against these attacks. While no personal financial information or credit card data was obtained, the hackers may have gained access to some user names, email addresses, and/or passwords. As a precaution, we recommend that all our fans immediately change passwords on all our sites — including our community forums and the statistics site we maintain for Brink players.
If your username/email address/password is similar to what you use on other sites, we recommend changing the password at those sites as well. As we don’t know what further plans the hackers may have, we suggest that you keep an eye out for suspicious emails and account activity.
We regret any inconvenience that these attacks on us cause for you. These attacks will be evaluated to determine if there are any additional protections we might take that would be prudent.

Sunday, May 29, 2011

DARKSIDERS 2

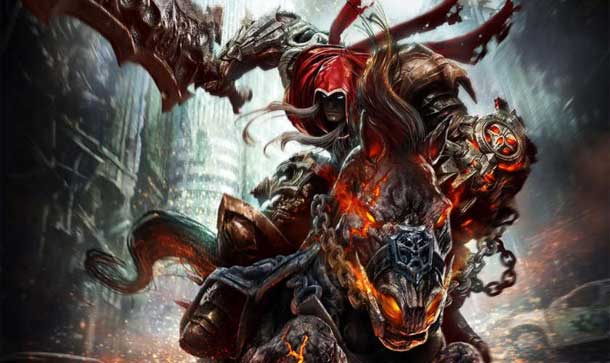
I recently started playing DARKSIDERS and found it to be a blast. Bought it at Gamestop, used, for just a couple dollars. Well worth it. I feel like I am playing a hybrid of GODS OF WAR and DEVIL MAY CRY. They even have a fun Website Darksiders. 
Now I am barely into the game, fought a couple Bosses and today I come across news for Daksiders 2.
Looks like it's been a rumor for over a year, but with E3 closing in, fresh info comes around for some of our favorite games and new titles.
Here's a little of what I found.


Darksiders 2 Info Probably On its Way


We may be getting an official Darksiders 2 announcement sometime between now and E3. Danny Bilson of THQ recently revealed that there is news on the game coming "in a big way". If there was any doubt that Vigil Games would be making a follow up to the 2010 Hack & Slash/Puzzle Platformer, you need not look further than the ending cut-scene to realize that the three other hor***** of the apocalypse have made their may to Earth.

Last November, Danny Bilson revealed that Darksiders 2 was definitely heading our way, when he made statements about the franchise at IGDA Leadership Forum.

QUOTED TEXT:  "“When we do the Darksiders sequel, it’ll be a different character and take place simultaneously to the other story. There’s only one apocalypse I couldn’t very well have four different apocalypses, one for each rider. It has some new mechanics and some very robust features that differentiate it a lot and grow it from the first game because you have to build on the first one, you can’t repeat it. I think that’s very important in franchise-building.”

The game which was said to be aiming for a 2012 release date could have a large prescence at E3.  The first game was recieved well as a first offering from Vigil games, and was thought to draw from The Legend of Zelda franchise as inspiration for the gameplay.  Coupled with the fantastic art behind the game, Darksiders was a great start to what could be a long running franchise.

Monday, May 23, 2011

PlayStation Network Hack Attack to cost Sony $171 million

PlayStation Network hacker attack to cost Sony $171 million


AS part of its revised earnings projections, published overnight, Sony said it estimates the April hacker attack on its PlayStation Network (PSN) will cost the company ¥14 billion, or $171 million. 
 
The cyberattacks, which kept the PSN offline for 23 days, involved the theft of personal data that included names, passwords and addresses from more than 100 million accounts on the online service.
The estimated cost to Sony includes the personal information theft protection program it launched after the attacks, the "Welcome Back" program to compensate customers for the outage, customer support, network security enhancement, legal experts and the impact on profits due to a possible future revenue decrease.
"So far, we have not received any confirmed reports of customer identity theft issues, nor confirmed any misuse of credit cards from the cyber-attack," the company said.
"Those are key variables, and if that changes, the costs could change."
Class action lawsuits have also been filed against Sony and some of its subsidiaries.
"However, those are all at a preliminary stage, so we are not able to include the possible outcome of any of them in our results forecast for the fiscal year," the company said.
The costs will be incurred during Sony's current fiscal year, which ends on March 31, 2012. The company will report results for fiscal year 2011 this Thursday.
The projections aren't good for the electronics giant, which today warned investors it would run some $3.2 billion in the red, the second consecutive year it has made a loss after a 13-year run of profits.
The projection of a net loss for the fiscal year ended March 2011 was largely due to writing off $4.4 billion related to a tax credit booked in the fourth quarter.
The company had earlier projected a $860 million profit.
Like many other Japanese manufacturers, Sony has been hampered by the production disruptions set off by the March 11 earthquake and tsunami that killed more than 25,000 people, destroyed many factories and sent the nation's economic recovery into reverse.
Sony has seen plunging sales of flat-panel TVs and other gadgets, and was likely to remain in the red in its TV business for the seventh year straight.
Sony has also taken a beating in music players and other portable devices to Apple's iPod, iPhone and iPad.